Meet Fortivra, continuously proving that enterprise security works
Fortivra is the AI-native platform for Autonomous Security Assurance - continuously proving that enterprise security works.
The problem
Enterprises invest heavily in cybersecurity, yet security leaders still struggle to answer a deceptively simple question: "Are we actually secure, compliant and resilient right now?"
Security environments change continuously: Controls drift, new vulnerabilities and threats emerge, regulations evolve and infrastructure changes. However, assurance is still largely based on periodic audits, manual assessments and point-in-time reports that can become outdated almost as soon as they are produced.
What Fortivra does
Fortivra is changing that. Its AI-native platform continuously validates whether security controls actually work, assesses compliance against regulations and standards, models emerging threats, adversarially tests resilience, quantifies cyber risk in financial terms, and supports the orchestration of remediation while also autonomously performing some remediations.
The result is continuous, evidence-based assurance: giving security leaders visibility into what is working, what is not, what matters most, and what to do next, before weaknesses become incidents.
How it started
Fortivra grew out of a question that repeatedly came up when working on engagements in clients from diverse industries:
Are we secure enough, compliant enough and resilient enough, right now, not a monthly, quarterly or annual posture view - right now
The uncomfortable reality was that this question was surprisingly difficult to answer. Organisations would invest heavily in security technology and then rely on consultants, auditors and internal teams to periodically assess whether those investments were actually working. By the time the assessment was completed and the report delivered, the environment had often already changed.
Meanwhile, attackers do not operate on an annual audit cycle.
That gap became the starting point for Fortivra: what if security assurance could become continuous rather than periodic - and autonomously intelligent rather than predominantly manual?
Fortivra was built to provide that continuously updated view of security, compliance, threat exposure and financial risk, while helping organisations act on weaknesses before they become incidents.
Why this team
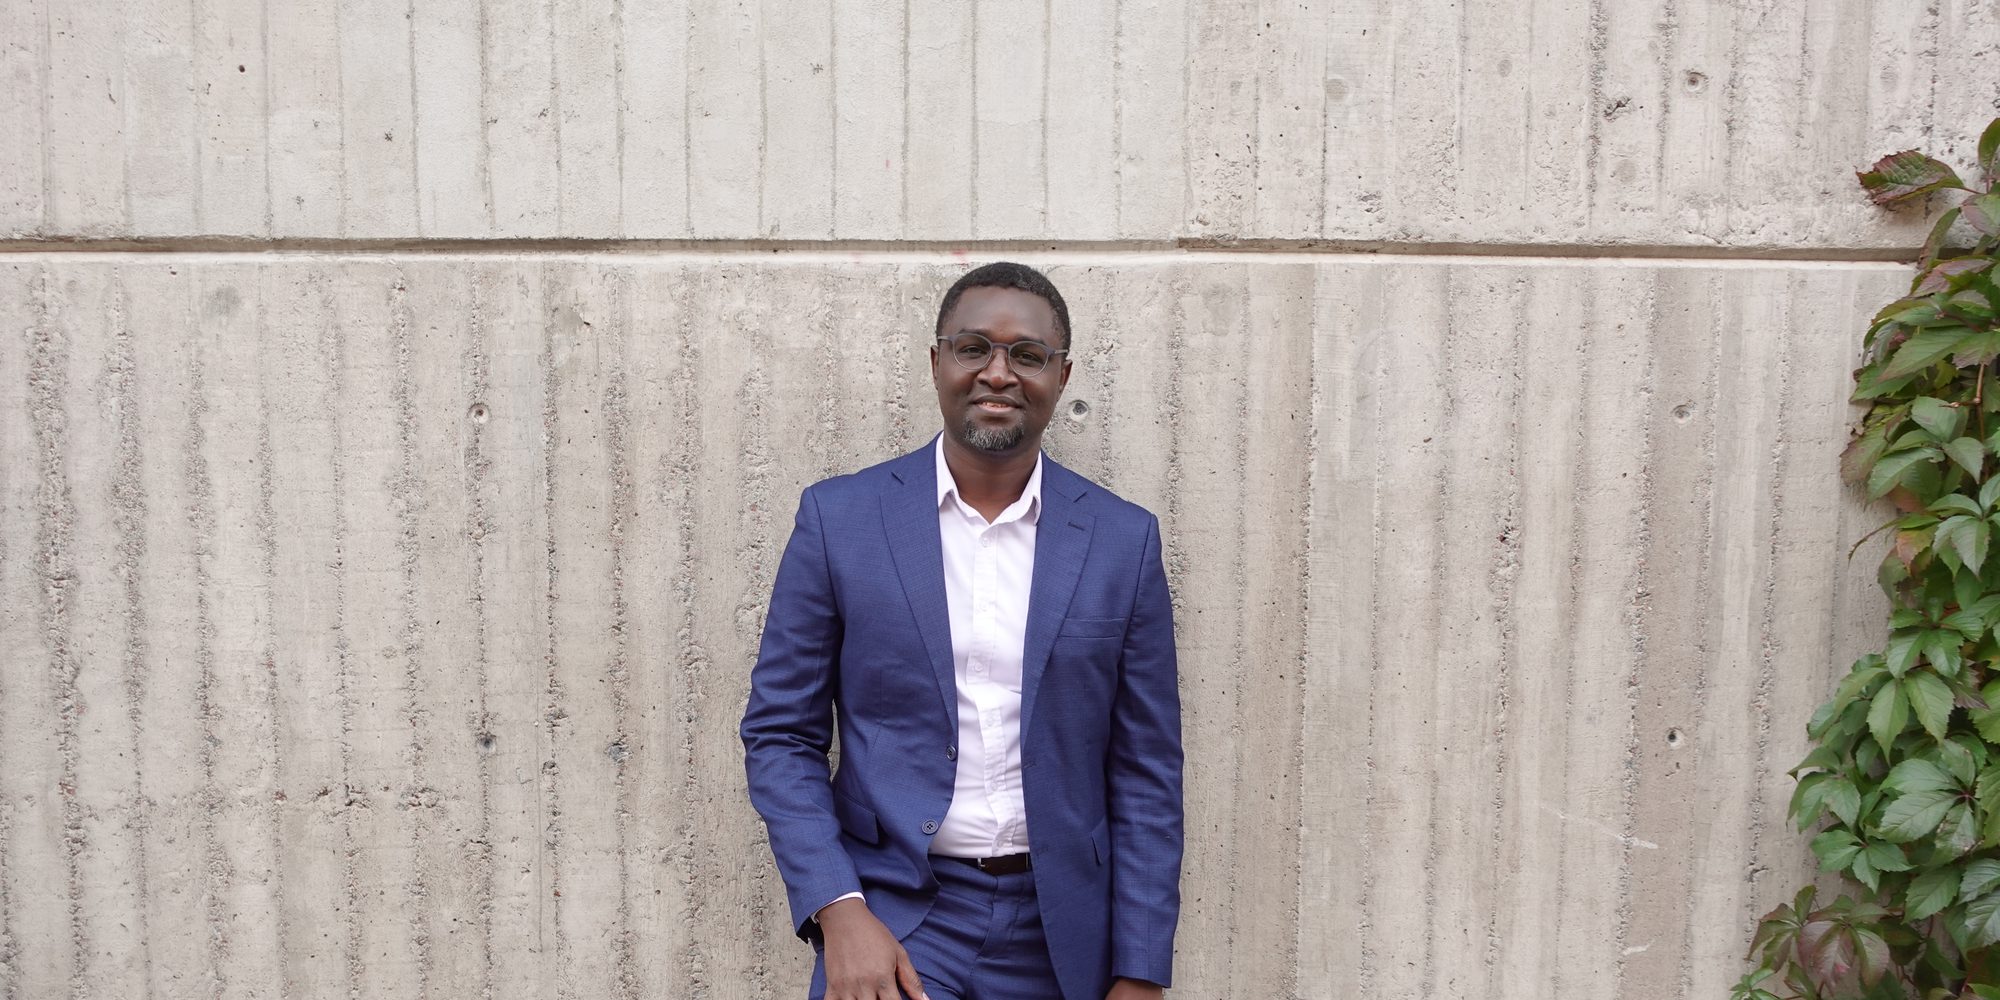
Founder and CEO Nashon Oginga brings more than 14 years of cybersecurity experience spanning security architecture and implementation, cyber resilience, risk management, regulatory compliance and security advisory.
Before founding Fortivra, Nashon held senior consulting and leadership roles at Deloitte and KPMG, leading complex cybersecurity engagements for large and regulated enterprises.
Co-founder and COO Sameer Sidhanti brings complementary experience in cloud security and cybersecurity advisory. Together with the wider founding team, Fortivra combines hands-on enterprise cybersecurity experience with the engineering and AI capabilities required to rethink how security assurance is performed.
Why Sting
We joined Sting at an important inflection point for Fortivra: moving from building the platform to validating it with leading enterprises, expanding our design-partner and pilot ecosystem, and preparing for commercial scale.
Sting gives us access to experienced founders and coaches, investors, enterprise partners and one of the strongest startup networks in the Nordics. We want to use that platform to challenge our thinking, accelerate our go-to-market, secure the right design partners and investors, and establish Autonomous Security Assurance as a new category in enterprise cybersecurity.
Nashon Oginga, Founder and CEO of Fortivra
Fortivra is one of 21 startups in Sting Core Fall 2026. Meet the rest of the cohort in Meet the 21 startups joining Sting this autumn.